Industries · Banking
Agents change bank systems. Unreviewed, that is an MRA.
Examiners sample program changes. Two officers certify the procedures each April. Every agent session is checked against SOX change control, Part 500, and your DPA.
Pre-production only: how agents change your systems, not how those systems run.
- CISO
- Head of Model Risk
- Internal Audit
- VP of Engineering
Approval queue
Illustrative · demo data
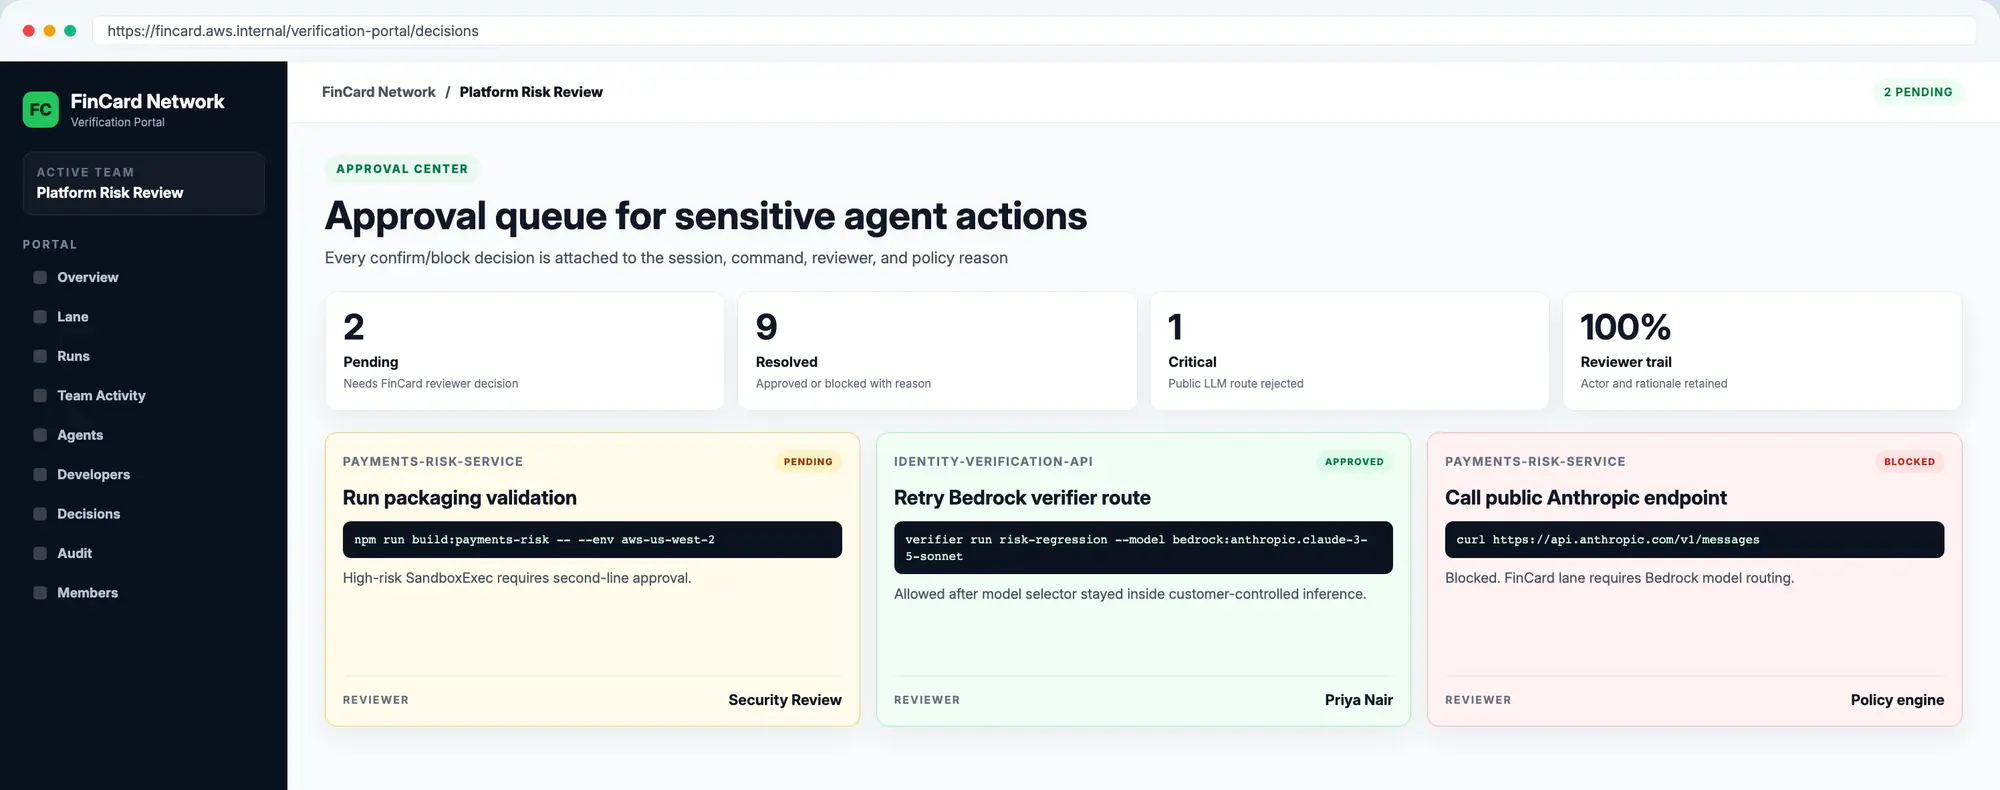
Each gated change names the reviewer, the decision, and the rule that fired.
Industry trend
83%
of developers use AI tools or agents at work
Stack Overflow 2026 (opens in a new tab)Oct 2026 · n = 17,464
24%
say their organization provides approved AI tools and guidance for using them
Stack Overflow 2026 (opens in a new tab)Oct 2026 · n = 13,167
6.6%
trust AI output for important work decisions
Stack Overflow 2026 (opens in a new tab)Oct 2026 · n = 14,304
Source: Stack Overflow Developer Survey 2026, self-reported; data under ODbL 1.0. AutoDevOps is not affiliated with Stack Overflow.
01Where agents meet your obligations
Three sessions your examiner will ask about.
01
An agent runs terraform apply against the payments network.
In review mode, the command waits for a reviewer. A self-approval opens a finding.
BASE.PROD-CHANGE-REVIEW02
An agent edits a reconciliation job that feeds the general ledger.
The approval names requester and reviewer. An approval with no named requester shows as unverified.
BANK.SOX-ITGC-CHANGE03
Customer account context reaches a model provider outside the DPA.
A critical finding names the provider, the session, and the clause.
BANK.NPI-PROVIDERS
02The authorization at stake
The examiner does not ask whether the agent was careful. They ask who approved it.
Part 500 exists because you hold a DFS authorization. Two officers certify it every April.
At stake
Charter and deposit insurance, and for DFS licensees the license that makes Part 500 apply. A fintech partner runs under its sponsor bank’s.
01
Exam sample
An agent change with no independent approver fails the sample.
02
Matter Requiring Attention
Deficiencies become MRAs with deadlines. The OCC’s principle is escalation.
03
Formal enforcement
Cease-and-desist orders, civil money penalties, removal of individuals. All public.
04
Certification and insurance
A certification the record cannot support is its own violation.
Sources: PCAOB AS 2201 (IT general controls); 23 NYCRR 500.8 · OCC Bulletin 2026-41 (PPM 5310-3, 5400-11) · 12 U.S.C. §1818(b), (e), (i)(2) · 23 NYCRR 500.17(b), 500.20 · Directive 2013/36/EU (CRD IV), Art. 18
Charter forfeiture is rare and never first. MRAs and consent orders are routine, and each starts with one unreviewed change. The record is evidence for your examiner, not a finding of compliance.
03Obligations checked
Every clause, checked on every session.
Review and forbidden-action rules hold the agent before it acts. Provider, data, and intent rules record after.
BASE.PROD-CHANGE-REVIEW
Infrastructure changes get an independent approver
Framework · SOC 2 Trust Services Criteria · CC8.1 (change management)
BANK.SOX-ITGC-CHANGE
Financial reporting code gets an independent reviewer
Regulation · SOX §404; PCAOB AS 2201 (IT general controls over program change)
BANK.NYDFS-APPSEC
Agent pushes to release branches get an independent approver
Regulation · 23 NYCRR Part 500 · 23 NYCRR 500.8 (application security)
BANK.CREDIT-MODEL-INTENT
Credit model changes carry documented intent
Internal policy · Model risk management policy · Customer MRM policy; EU AI Act Annex III point 5(b)
BANK.NPI-PROVIDERS
Customer financial data reaches covered providers only
Regulation · Gramm-Leach-Bliley Act · GLBA §501(b); 12 CFR 30 App. B §III.D (banks); 16 CFR 314.4(f) (non-bank financial institutions)
PAY.PCI-CODE-REVIEW
Payment code is reviewed by someone other than the author
Framework · PCI DSS v4.0.1 Req. 6.2.3; 6.2.3.1 for manual reviews
Plus 4 baseline obligations every pack checks
BASE.SECRET-CONTEXT
Credentials stay out of agent context
Framework · ISO/IEC 27001:2022 · Annex A 5.17 (authentication information)
BASE.DPA-PROVIDERS
Model calls stay on the DPA subprocessor list
Contract · Customer data processing agreement · DPA subprocessor schedule
BASE.AGENT-SYSTEM-REVIEW
Agent prompts, tools, and guardrails get an independent reviewer
Internal policy · AI system change policy · Customer AI system change policy; EU AI Act Art. 14 (human oversight)
BASE.NO-FORCE-PUSH
Agents never rewrite shared history
Internal policy · Secure development standard · Protected branch policy
Templates ship without dollar figures; the register shows a labeled illustrative band until you add yours. Pre-run checks use review mode, a customer-cloud CLI capability.
04Controls evidenced
Controls this evidence supports.
From the public control catalog. Evidence mappings do not establish compliance.
- FFIEC.SOD-01Separate review dutiesInformation Security booklet: separation of dutiesEvidence mapping
- FFIEC.SDLC-02Change attributionDevelopment, Acquisition, and Maintenance booklet: change managementVerifiable artifact
- NYDFS.APP-01Secure development evidenceSection 500.8: application securityEvidence mapping
- NYDFS.TPSP-03Third-party providersSection 500.11: third-party service provider security policyReview signal
- DORA.CHG-04Change approval recordArticle 9(4)(e): change managementVerifiable artifact
- SOC2.CC8-03Change evidence integrityTrust Services Criteria CC8: change managementVerifiable artifact
05For your risk and insurance reviewers
Evidence an AI liability underwriter can rate.
- Verified controls
- Gate coverage, independent review rate, and self-approvals.
- Change velocity
- Weekly changes to prompts, tools, or guardrails, and the share with a stated reason or approval.
- Autonomy
- Unattended sessions and the allow, hold, and block mix.
- Obligation posture
- Findings by status, priced per obligation.
Production behavior is out of scope and marked that way. The packet is evidence for a reviewer. It is not insurance, a certificate of coverage, or a premium quote.
Sources and citations · 5 rules referenced
- Sarbanes-Oxley Act §404
PCAOB AS 2201: IT general controls over program change
- 23 NYCRR Part 500
§500.1(e) covered entity; §500.8 application security; §500.11 third-party service providers; §500.17(b) annual certification
- Gramm-Leach-Bliley Act
§501(b); Interagency Guidelines Establishing Information Security Standards, 12 CFR 30 App. B §III.D
- Interagency third-party risk guidance
Third-Party Relationships: Risk Management (June 2023)
- EU AI Act
Annex III point 5(b): creditworthiness and credit scoring
Your institution confirms which systems are in SOX scope, which Part 500 class applies, and which providers your contracts cover. Findings are evidence for that review, not a conclusion. For your counsel and compliance team, not legal advice.
Other industries: Insurance, Healthcare, Payments.
Bring one banking obligation
We run it against your agents’ recorded sessions and hand you the findings, priced exposure, and evidence packet.